Yesterday, I was alarmed to learn that LTS versions of Ubuntu are still lacking a critical security update to patch a severe vulnerability that was first disclosed on October 15th. As of now, all LTS versions dating back to version 16.04 have this vulnerability.
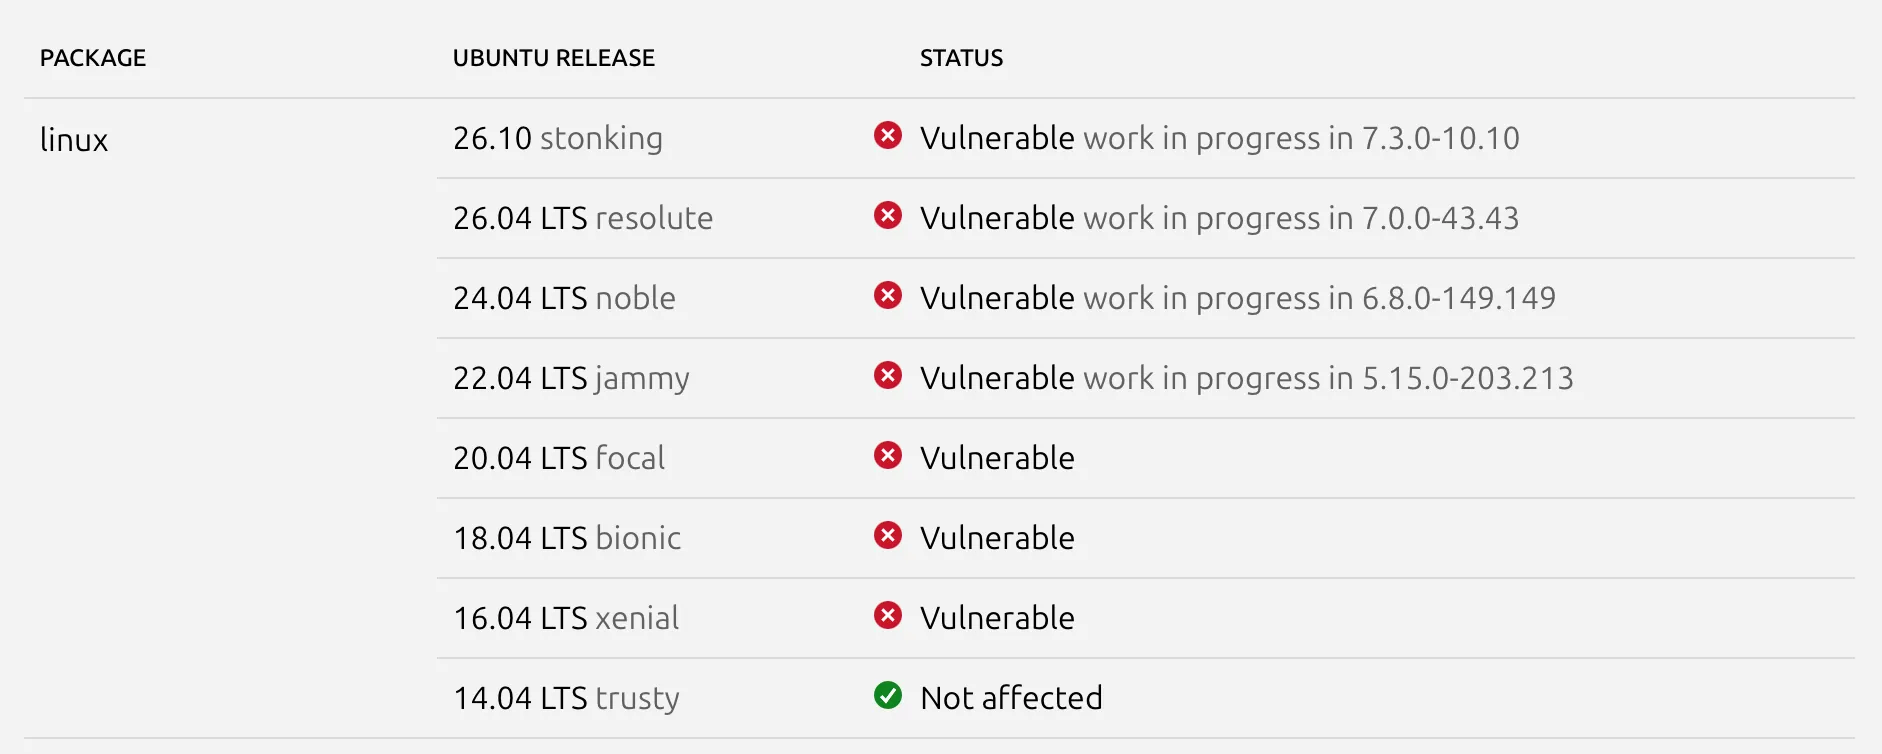
Until recently my Hetzner VPS ran Ubuntu. Even though it’s unlikely that I would fall victim to this vulnerability, I find it unacceptable that Canonical are taking this long to ship a security patch. To be fair, Canonical did recommend a mitigation for this but it only reduces the risk.
My bigger worry is that we’re starting to see more and more vulnerabilities being disclosed at a pace that’s hard to keep up with. Last month alone was bad enough that it’s now referred to as Black October. Given that AI will only accelerate this trend, I’m finding that it’s now more critical than ever to keep systems, like my VPS, up-to-date on the latest security patches as quickly as possible.
So I reconfigured my VPS to run Debian instead, which already received a security patch the day after the CVE was announced. While this incident alone may not be proof that Debian will always have faster updates, it’s been enough to tip me over the edge.